HQ NORCROSS, GA · 470-284-5400
Critical Technology Services
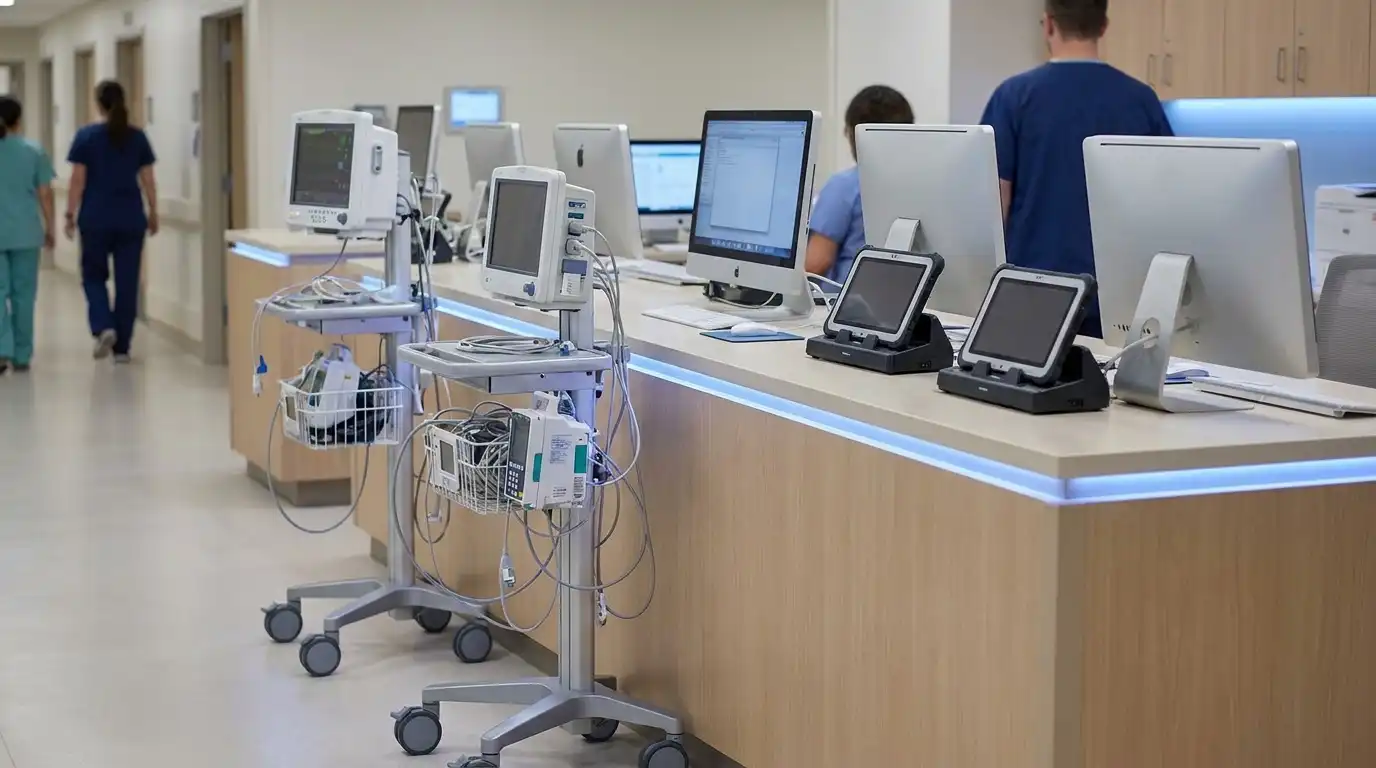
A hospital IT environment: medical-grade computers and tablets at a nursing station with networked patient-monitoring equipment.
INDUSTRY

Healthcare.

HIPAA chain of custody. Medical device retirement. An audit-ready trail.
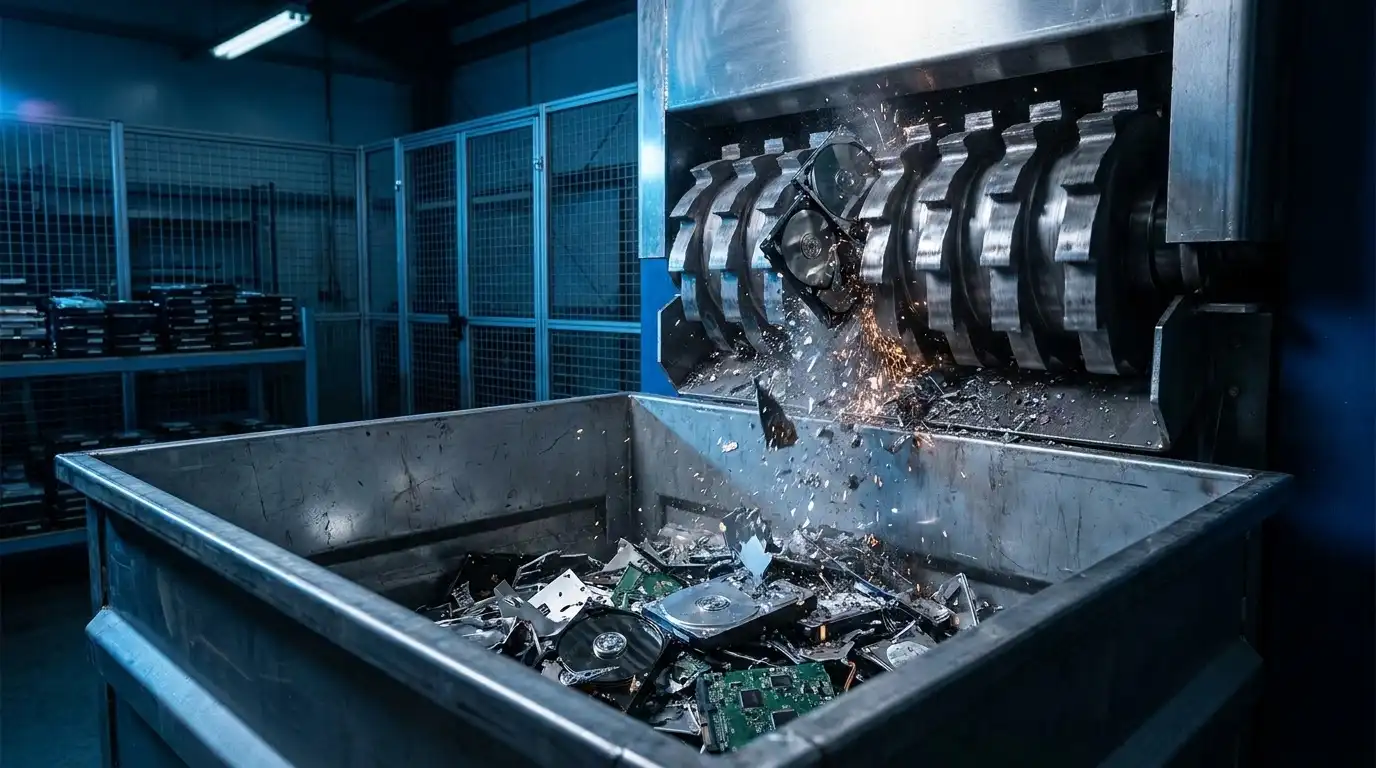
An industrial hard-drive shredder destroying disk drives, shredded metal fragments falling into a steel collection bin.
THE PROBLEM

Patient data hides in more than the obvious places.

Healthcare IT spans clinical workstations, imaging gear, and connected medical devices, all of it potentially holding ePHI, all of it under HIPAA. CTS retires it with a serial-level chain of custody and a HIPAA-ready audit trail, so the device leaving your building is a documented event, not a liability.

WHAT WE HANDLE

Built for HIPAA-regulated environments.

HIPAA chain of custody

Every device that touched ePHI is tracked by serial number from pickup to destruction, with a certificate per device, the trail an OCR audit expects.

Connected & medical device retirement

Imaging systems, clinical workstations, and connected devices often store patient data in non-obvious places. We identify, sanitize, and document each one.

NIST 800-88 data destruction

Drives are wiped to NIST 800-88 or physically shredded, with a certificate of destruction tied to the serial number.

One audit-ready report

Disposition, data destruction, and ESG metrics roll up into a single report your compliance team can hand to an auditor.

Learn more about HIPAA compliance obligations in our guide to HIPAA data destruction requirements and explore our certified hard drive shredding services.

FAQ

Healthcare ITAD questions we get a lot.

01

How does CTS support HIPAA compliance when we retire hardware?

Every device that touched ePHI is tracked by serial number from pickup through destruction, and each one gets its own certificate of destruction. That serial-level chain of custody is the documented trail an OCR audit expects, so a retired device becomes a recorded event rather than a compliance gap.
02

Do you provide a certificate of destruction per serial number?

Yes. Each drive we wipe or shred gets its own certificate tied to the serial number, so your audit trail maps to individual assets instead of a single bulk statement.
03

How do you handle connected medical devices and imaging systems?

Imaging systems, clinical workstations, and connected medical devices often store patient data in non-obvious places. We identify each one, sanitize the media to NIST 800-88 or physically destroy it, and document the disposition per device.
04

Is CTS R2v3 certified?

Yes. CTS is an R2v3-certified IT asset disposition operator, and also holds ISO 14001, 9001, and 45001. Data is destroyed to NIST 800-88, with physical shredding to under 2mm when destruction is required.
05

Can you handle pickups across multiple hospitals or clinic sites?

Yes. We offer national coverage and multi-site pickups, so a health system with hospitals, clinics, and admin offices runs one contract and one chain of custody across every location.
06

What happens to healthy drives and devices we retire?

Drives that pass verification can be wiped to NIST 800-88 and the equipment resold or redeployed, with any residual value returned to you. We destroy only what is failed or too sensitive to reuse.
READY TO START?

Retire healthcare hardware without the audit risk.